
1. What is OpenClaw 2.0 and why this update is a game changer
The autonomous AI agent ecosystem is advancing at breakneck speed, and open-source project OpenClaw has just crossed a historic milestone. Available on its official GitHub repository, major release OpenClaw 2.0 (tagged 2026.8) represents the largest overhaul in the project’s entire history.
Unlike standard chatbots confined to a browser tab, OpenClaw operates as a proactive, self-hosted autonomous assistant on your own machines. It can execute terminal commands, manage local files, schedule background workflows, and connect directly to everyday productivity tools as well as messaging platforms like Telegram, Discord, and WhatsApp.
Release 2.0 completely rethinks user experience, technical architecture, and security. In this comprehensive guide, we will break down what is new in OpenClaw 2.0, understand why isolating an autonomous agent on a remote server is essential for your security, and walk step-by-step through installing OpenClaw 2.0 on a Linux VPS before connecting its graphical interface (GUI) from your personal computer using modern, automated workflows.
If you already followed our practical OpenClaw installation guide on a Linux VPS, this tutorial focuses on version 2.0 and connecting the PC interface.
2. Key differences between OpenClaw 1 and OpenClaw 2.0
OpenClaw 2.0 goes far beyond minor adjustments. Built by over 930 contributors and merging more than 16,000 pull requests (accounting for roughly half of the repository’s total history), this release introduces architectural transformations:
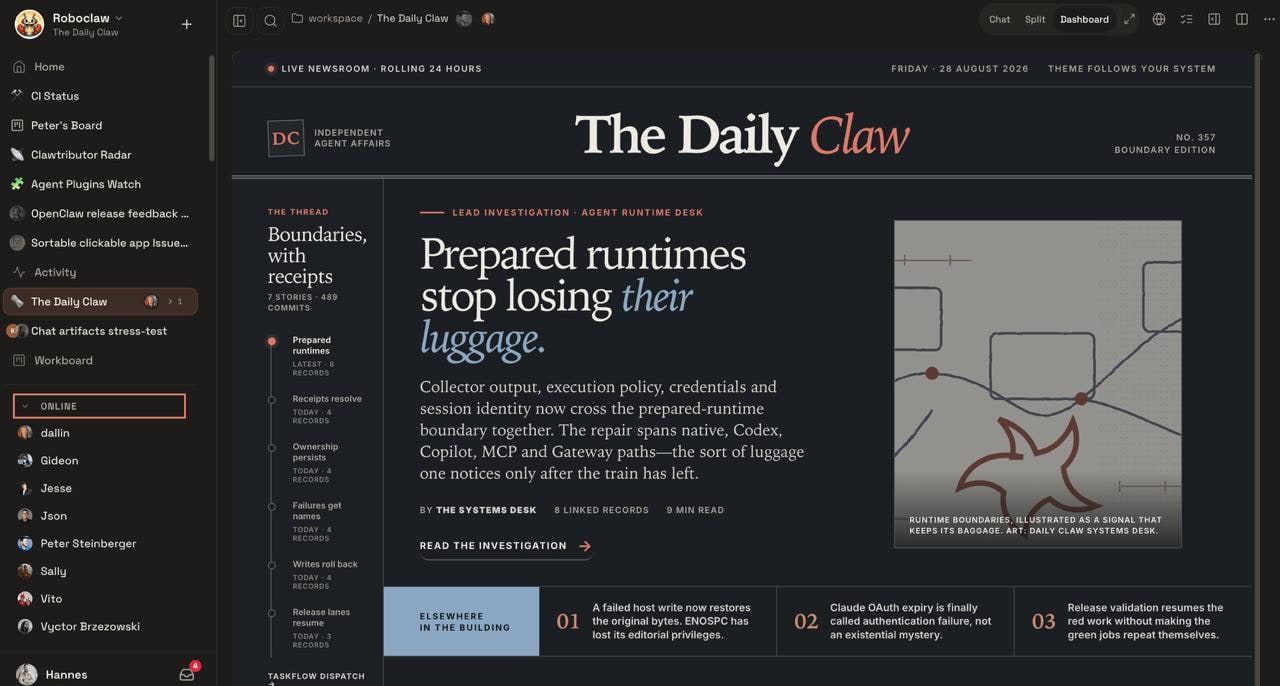
- Rebuilt Control UI: the browser interface was redesigned from the ground up using Vite and Lit. It now opens instantly into a sleek workspace featuring a collapsible Home side drawer, allowing you to chat with your agent without navigating away from ongoing tasks.
- Automated and streamlined onboarding: the installer automatically detects existing model subscriptions (OpenAI, Claude), API keys, or local models already available on your system.
- Shared Multiplayer cloud sessions: OpenClaw introduces collaborative sessions in the cloud. You can bring team members into an active session or hand over an ongoing task with all context and history preserved.
- SQLite persistence migration: session storage and conversation transcripts have migrated away from loose JSON files into a robust, transactional SQLite database (
openclaw-agent.sqlite), delivering significantly improved speed and reliability. - First-class desktop companion apps: the ecosystem now features dedicated desktop applications (Windows Hub built with WinUI, native macOS app, and Linux Tauri companion), designed to serve as remote controls (Remote Gateway) without requiring manual command lines in daily use.
With these enhancements, OpenClaw transitions from an experimental CLI tool into a modern, accessible collaborative platform for developers and power users alike.
3. Why run OpenClaw on a remote VPS instead of your local PC?
Before jumping into the installation, understanding the recommended architecture for running an autonomous AI agent is critical.
The real risk of running an autonomous agent on your personal computer
Autonomous AI agents like OpenClaw interact directly with the operating system: they execute shell commands, read and write files, perform network requests, and run code. Giving an agent unrestricted access to your daily work machine creates severe security risks:
- Accidental file corruption: an AI hallucination or a misunderstood instruction could accidentally overwrite important projects, delete sensitive documents, or alter operating system configurations.
- Data exfiltration and prompt injection: if your agent ingests emails, unvetted web pages, or public chat messages, an indirect prompt injection attack could instruct it to inspect local SSH keys, read browser cookies, or leak saved credentials.
- Task interruptions: personal computers frequently enter sleep mode, reboot for system updates, or switch Wi-Fi networks, which abruptly terminates background routines and messaging listeners.
The ideal solution: a dedicated Linux VPS as an isolated 24/7 sandbox
Deploying OpenClaw Gateway on a dedicated Linux VPS solves all of these challenges:
- Total sandbox isolation: the VPS acts as an airtight container. Even if the agent tests risky scripts or makes an error, your personal machine and private data remain strictly untouched.
- Uninterrupted 24/7 availability: hosted in a high-availability datacenter, your VPS never sleeps. Your automations, scheduled cron jobs, and message listeners continue running around the clock.
- The optimal hybrid setup: you enjoy the fluid experience of a modern desktop GUI on your personal computer while delegating heavy and secure execution to your isolated Linux VPS.
4. Prerequisites
To follow this tutorial, you will need:
- a Linux VPS (Ubuntu 24.04/22.04 or Debian 12 recommended) with root access via SSH
- a personal computer running Windows, macOS, or Linux to host the desktop interface
- an API key from an AI model provider (OpenAI, Anthropic Claude, Google Gemini, Groq, DeepSeek, or OpenRouter)
5. Step 1: Install OpenClaw 2.0 on the Linux VPS
Connect to your Linux VPS via your local terminal over SSH:
ssh root@your-vps-ip
Official script installation
OpenClaw 2.0 provides an all-in-one official installation script. It automatically detects your distribution, installs the required Node.js runtime if necessary, deploys the latest OpenClaw release, and sets up the background service:
curl -fsSL --proto '=https' --tlsv1.2 https://openclaw.ai/install.sh | bash
During the initial configuration wizard:
- For network binding (Gateway Bind), choose
loopback(127.0.0.1): this ensures the gateway only listens locally on the server and remains completely protected from the public internet. - Keep the default port
18789. - Choose
tokenauthentication. - Confirm background daemon registration (Install daemon).
(If you prefer running onboarding directly without interactive prompts, use openclaw onboard --non-interactive --accept-risk --flow manual --auth-choice skip --gateway-bind loopback --gateway-auth token --install-daemon).
To ensure OpenClaw continues running continuously after your SSH session disconnects, enable systemd lingering:
sudo loginctl enable-linger $USER
Verify that the Gateway service is active:
openclaw gateway status
The output should show Runtime: running (pid ..., state active), listening on 127.0.0.1:18789.
Retrieve your gateway authentication token from the configuration file:
cat ~/.openclaw/openclaw.json | grep -A 4 '"gateway"'
Copy the "token" value carefully, as you will need it to connect your PC.
For purists: Step-by-step manual CLI installation (NodeSource repo & npm)
If you prefer installing and managing each component individually via official package managers:
-
Update packages and install prerequisites:
sudo apt update && sudo apt upgrade -y sudo apt install -y curl git -
Install Node.js 24 from the official NodeSource repository:
curl -fsSL https://deb.nodesource.com/setup_24.x | sudo bash - sudo apt install -y nodejs -
Install the global OpenClaw 2.0 package:
sudo npm i -g openclaw@latest -
Launch onboarding and register the service daemon:
openclaw onboard --install-daemon
sudo loginctl enable-linger $USER
6. Step 2: Install OpenClaw 2.0 on your PC or Windows workstation
The OpenClaw 2.0 core is now running continuously on your remote server. You can install the graphical control center or client CLI environment on your personal computer.
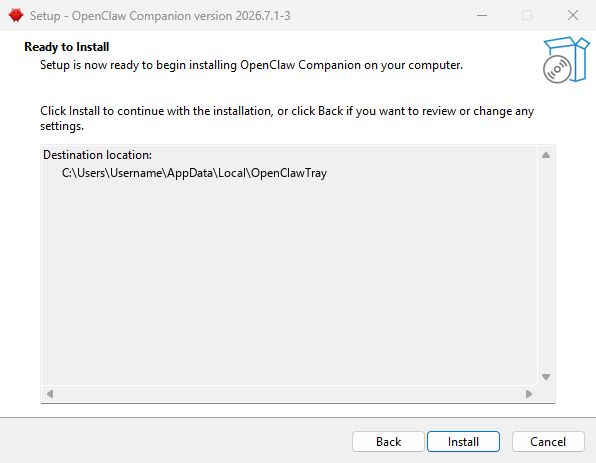
On a Windows workstation, start with OpenClaw Companion (Windows Hub), the WinUI desktop app. The official installer is still named Companion: it is not the npm CLI. The version shown in the wizard (for example 2026.7.1-3) can differ from the 2026.8 engine already running on the VPS.
Official desktop installers and companion apps are also available on the project documentation portal and directly on the official GitHub releases page:
- Windows: for the graphical interface, download the OpenClaw Windows Hub installer (Companion executable for x64 or ARM64). For the CLI only, you can also run
iwr -useb https://openclaw.ai/install.ps1 | iexin PowerShell. The WinUI app features system tray widgets, health diagnostics, and automated remote tunnel management. - macOS: download the native OpenClaw for macOS package (.dmg) from the official GitHub releases and drag it into your Applications folder. It features integrated remote gateway forwarding.
- Linux: download the OpenClaw Linux companion app as a standalone
.AppImageor.debpackage from the GitHub releases.
7. Step 3: Connect your local PC interface to the remote VPS
For security, we configured OpenClaw to listen strictly on the local loopback address (127.0.0.1) of the VPS. Your personal computer communicates with the server over an encrypted channel.
Direct connection through the desktop application
The OpenClaw 2.0 desktop companion apps (Windows Hub, macOS, Linux) feature integrated remote tunnel management:
- Launch your OpenClaw desktop app on your PC.
- On the welcome screen or under the Connections tab in settings, select Remote over SSH (or SSH-tunneled Gateway).
- Enter your remote SSH target:
(or your configured SSH alias fromroot@your-vps-ip~/.ssh/config). - Paste the Gateway Auth Token retrieved in Step 1.
- Click Connect.
The app establishes, encrypts, and maintains the SSH tunnel automatically in the background without keeping any open terminal window on your desktop.
Approve the device pairing request
On the very first connection from a new computer, OpenClaw 2.0 enforces a hardware security check: your PC interface displays a Device pairing required notification.
Once your local openclaw.json configuration points to your gateway URL (ws://127.0.0.1:18789) with your authentication token, verify connectivity using openclaw status:
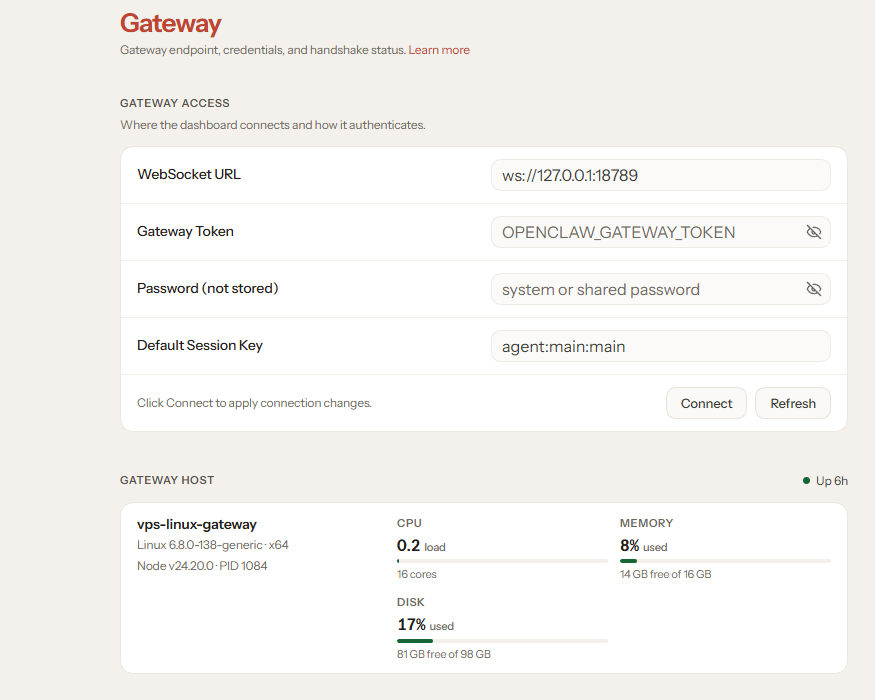
To authorize your computer, return to your VPS SSH session, list pending requests, then approve the exact identifier shown:
openclaw devices list
openclaw devices approve --latest
openclaw devices approve <requestId>
openclaw devices approve --latest only previews the most recent request. openclaw devices approve <requestId> is what actually approves it. After a successful approval, the desktop app status turns green. If the app already shows a connected state, there is nothing pending.
For tinkerers: Manual CLI tunnel and standard web browser method
If you prefer not to install any app on your personal computer, want complete control in your terminal, or simply want to use your regular web browser (Chrome, Firefox, Edge, Safari):
- Open a command prompt or terminal on your PC (PowerShell on Windows, Terminal on macOS/Linux) and launch the encrypted tunnel:
Start-Process ssh -ArgumentList "-N -L 18789:127.0.0.1:18789 -i C:\Users\Username\.ssh\id_ed25519 root@your-vps-ip"
Test-NetConnection -ComputerName 127.0.0.1 -Port 18789
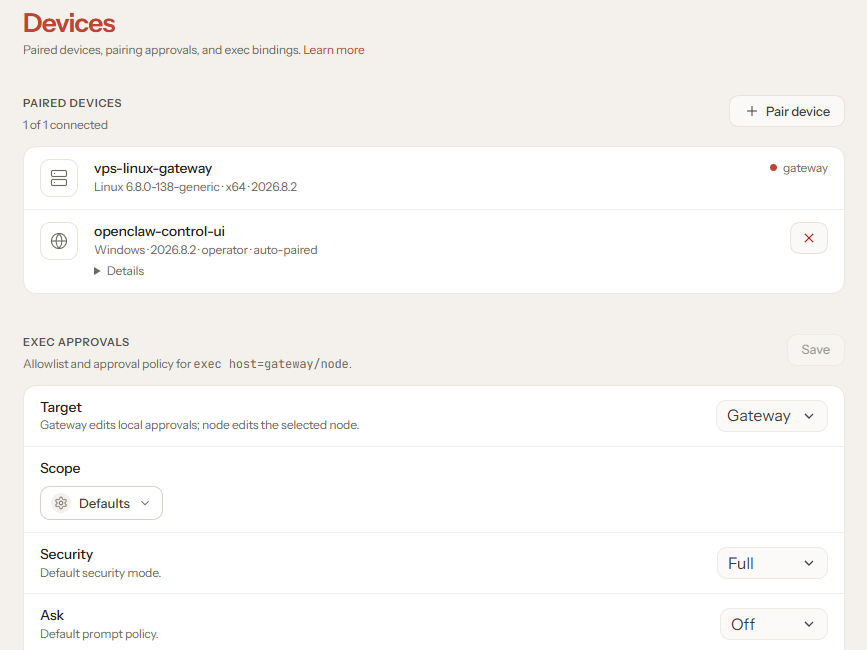
-N instructs SSH to maintain port forwarding without launching a remote shell, and -L securely redirects local port 18789 to the server’s loopback interface. Test-NetConnection immediately confirms the encrypted channel.
-
Open your browser to
http://127.0.0.1:18789/. -
On the Control UI welcome screen, select Remote Gateway, enter
ws://127.0.0.1:18789, paste your authentication token, and click Connect. -
On the VPS, list requests with
openclaw devices list, preview withopenclaw devices approve --latest, then approve withopenclaw devices approve <requestId>.
Advanced option: Remote web access with Nginx and HTTPS
If you want to access your dashboard from any computer without an SSH tunnel, you can place an Nginx reverse proxy with TLS (HTTPS) in front of OpenClaw.
Install Nginx and Certbot on your server:
sudo apt install -y nginx certbot python3-certbot-nginx
Create a virtual host under /etc/nginx/sites-available/openclaw proxying traffic to http://127.0.0.1:18789 with WebSocket upgrade headers (Upgrade and Connection), then generate your TLS certificate:
sudo certbot --nginx -d openclaw.your-domain.com
In ~/.openclaw/openclaw.json, configure the allowed origin and trusted proxy:
{
  "gateway": {
    "controlUi": {
      "allowedOrigins": ["https://openclaw.your-domain.com"]
    },
    "trustedProxies": ["127.0.0.1/32", "::1/128"]
  }
}
Restart with openclaw gateway restart. You can now connect directly from https://openclaw.your-domain.com.
8. Step 4: Remote-control your Linux server and run your first tasks
Your desktop app is now fully paired with your remote Linux server. You can also inspect the engine from your PC terminal:
openclaw gateway call health --json
The JSON response confirms that the request leaves your PC and is handled by the OpenClaw runtime on the Linux VPS (/root/.openclaw/agents/main/agent/openclaw-agent.sqlite).
The next screen is not that JSON: it is the Models view. Open Settings, then AI & Agents > Models, to add your providers:
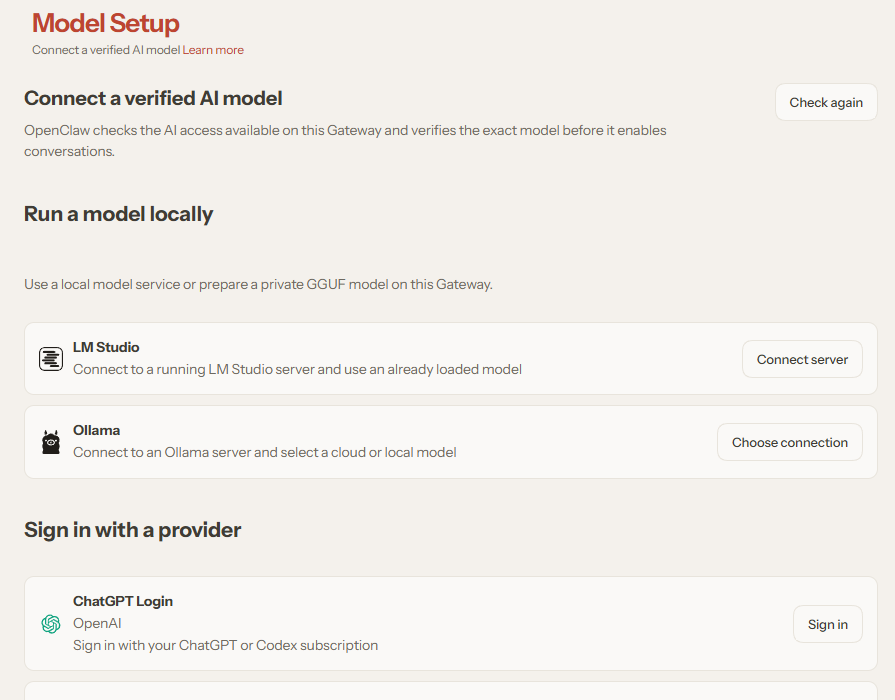
- Inside your desktop app, open Settings, then navigate to AI & Agents > Models.
- Click on your provider (OpenAI, Anthropic, Gemini, Groq, Mistral, or another compatible provider).
- Paste your key into
Model Provider API Key. - Select your preferred model (such as GPT-5, Claude Sonnet 4.6, or Gemini 2.5 Pro).
- Save your configuration.
Switch to the Chat tab and send your first prompt: OpenClaw processes your instructions, executes its tools directly inside the isolated environment of your Linux VPS, and streams responses to your screen in real time.
9. Essential daily administration commands
To manage your OpenClaw 2.0 instance over time, keep these practical commands handy:
- Follow live gateway logs:
openclaw logs --follow - Restart the gateway service:
openclaw gateway restart - Update OpenClaw to the latest release:
openclaw update openclaw gateway restart - Create an archive backup of settings and SQLite database:
openclaw backup create - Audit overall system health:
openclaw doctor
10. Summary and next steps
OpenClaw 2.0 sets a new standard for self-hosted autonomous AI assistants. By decoupling the visual cockpit (on your personal computer) from the execution engine (on an isolated Linux VPS), you combine the fluid ease of a modern graphical interface with total protection for your sensitive data and local files.
If you are looking for reliable, high-performance infrastructure to deploy OpenClaw 2.0 with instant delivery, you can deploy your Linux VPS at BoxToPlay and launch your always-on autonomous agent in minutes.
More Articles
BoxToPlay Updates: Custom Notification Center and Real-Time Alerts
September 24, 2026BoxToPlay Mobile V3: Widgets and Alerts for iOS and Android
September 21, 2026How to install Portainer on a Linux VPS
August 27, 2026Block ads on all your devices: 4 solutions for a Linux VPS
August 18, 2026